What Is an AI Audit and Does Your Business Need One?
An AI audit is a structured review of where your business uses AI, what data those tools touch, what rules govern them and whether any of it is saving time or money.
Microsoft research published in October 2025 found that 71% of UK employees have used unapproved consumer AI tools at work and 51% do so every week. Censuswide surveyed 2,003 UK employees for Microsoft. If you run a 30-person firm, someone in your team has probably pasted a client email into a free chatbot this month. You would not know and your insurer or your largest customer might ask.
What an AI audit covers
A useful audit has three layers. Each one answers a different question and skipping any of them leaves a gap.
The usage layer: what AI is actually in use
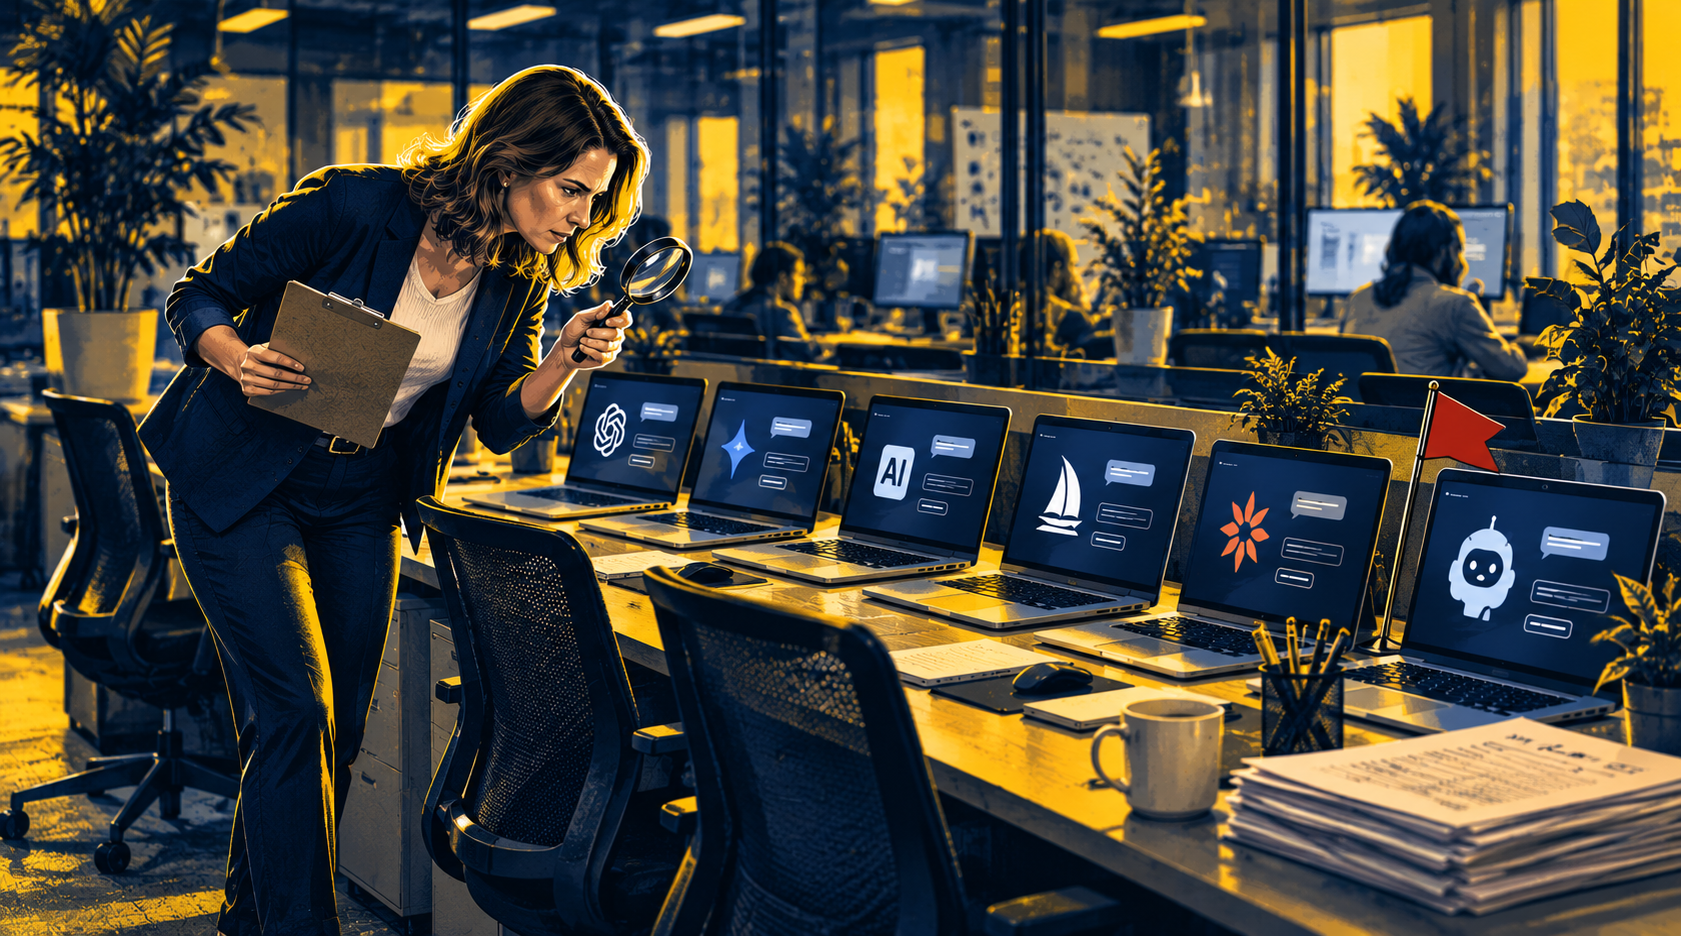
The first layer is a register of every AI tool used in the business. It lists the tool, the team using it, the task, whether the licence is paid or free and who approved it.
Official surveys will not give you this picture. The government's AI adoption research states that its survey does not provide insight into shadow AI, meaning use outside formal oversight, because it interviewed the person who oversees technology. Your own staff are the only reliable source. Our guide to what shadow AI is and how it spreads shows how to ask without blame.
The data and systems layer: what AI can reach
The second layer checks what information the tools see and where your records live. Gartner found that 63% of organisations either lack the right data management practices for AI or are unsure whether they have them. They predict that organisations will abandon 60% of AI projects unsupported by AI-ready data through 2026.
For an BUSINESSS this layer is practical. Which spreadsheets hold customer details? Which shared drives have no access limits? Which supplier systems feed your reports? Our article on signs of tech debt lists the warning signs that AI will inherit.
The risk and compliance layer: what the rules require
The third layer checks your use of AI against the law and your contracts. Three areas matter most for Businessses.
The first is data protection. The Information Commissioner's Office (ICO) say that AI use involves processing likely to result in a high risk to individuals, which will usually trigger a data protection impact assessment. The same guidance places overall accountability with your organisation as the controller and it adds that senior management share responsibility for AI risk and cannot hand it to data scientists or engineers. The ICO have marked the page as under review because of the Data (Use and Access) Act. Check it before you rely on it.
The second is supplier contracts. The ICO state that a written contract is needed every time a controller uses a processor for personal data. Their AI audit toolkit on contracts and third parties goes further and recommends documenting whether each party is a controller or a processor, checking accuracy and bias evidence before you buy and including audit rights in the contract. A free chatbot account taken out by an employee has none of that.
The third is the EU AI Act, which applies if you sell into the EU. The Digital Omnibus on AI entered into force on 27 July 2026. It moved the date for stand-alone high-risk systems from 2 August 2026 to 2 December 2027. It also changed the AI literacy duty in Article 4 so that providers and deployers must take measures to support AI literacy rather than guarantee a sufficient level. The duty has applied since 2 February 2025. Our posts on what Businessses must do now under the EU AI Act and whether the Act affects you explain the detail.
AI audit, readiness assessment and workshop: how they differ
Owners often mix these three up and the confusion costs money.
An AI readiness assessment is a quick score of how prepared you are. Ours takes two to three minutes, is free and returns a personalised report straight away. It gives you a starting point. It relies on your answers and does not inspect your tools or contracts. It cannot replace an AI audit.
An AI audit looks at evidence. It checks what is in use, what data it touches and what the paperwork says.
An AI workshop looks forward. It finds the tasks where AI could save money and ranks them. Our guide to the benefits of an AI readiness assessment and our explanation of what an AI workshop is show where each one fits.
In our view the order should be assessment, then audit, then workshop. Most Businessses do the workshop first, buy a tool and audit the damage afterwards.
What a good AI audit report contains
Whether you run the audit yourself or hire an adviser, the output should fit on a few pages. A good report contains five items: the register of tools, a risk rating for each one, the gaps in contracts and data controls, a short list of fixes in priority order and a named owner for each fix.
Take a small accountancy practice as an illustration. The register might show that two partners use a general chatbot to draft client letters, the payroll team use an AI feature inside their software and a junior has installed a meeting recorder. The risk rating flags the recorder as red, because it stores client conversations with a supplier that has no contract in place. The fix list puts a contract check first and a staff briefing second. Each fix takes days and none needs new software.
Be wary of any report that ends with a recommendation to buy a tool. An audit finds problems. Choosing a solution is a separate piece of work and mixing the two creates a conflict of interest.
Does your business need an AI audit?
You need an AI audit now if any of these apply. Staff use AI tools and you have no written policy. Customer, employee or financial data could have entered a prompt. A client or a tender asks how you use AI. You sell into the EU. You have paid for AI tools for three months or more and cannot state what they saved.
You can wait if nobody in the business uses AI and you have no plans to start. Write a one-page policy, take the readiness assessment and revisit in six months. If you are at the start of the AI confidence journey, this is the sensible order. Waiting is sometimes the right answer and we will tell you so.
The objection: an AI audit is bureaucracy for a small firm
The fair objection is that audits sound like consultants billing for paperwork and businesses of 20 people have no compliance department.
The answer is to scale the audit to the business. Firms of 20 people do not need a 40-page report. They need a register of tools, a short list of data rules and a named owner. A half-day with your office manager and a spreadsheet covers it. Our article on AI risk management for Businessses shows the proportionate version.
How to run a basic AI audit in one afternoon
You can run a first-pass review yourself this week. This is the test we would run first.
Start with an amnesty. Tell the team that nobody will be disciplined for listing the AI tools they use and ask them to write down the tool, the task and the type of data involved. Check expense claims, browser extensions and software invoices for anything they forget.
Next, sort each tool into three groups. Green means paid, approved and used with no personal or confidential data. Amber means it works but needs a rule, such as removing client names before pasting text. Red means it handles confidential or personal data without a contract and must stop or move to an approved alternative.
Then write three rules on one page: which tools are approved, what data stays out of prompts and who signs off new tools. Our guide to the AI policy every BUSINESSS needs gives you a starting structure. Finally, put a review date in the diary. Tools change faster than annual reviews so we suggest every six months.
This self-run review will not replace specialist legal advice on personal data or EU obligations. It does show you where to focus that advice, which saves money.
Frequently asked questions
What is an AI audit?
An AI audit is a review of the AI tools your business uses, the data they access and the rules around them. It usually covers three things: what is in use, what data it touches and whether you meet your legal and contractual duties.
How much does an AI audit cost?
The cost depends on scope and on who carries it out. A self-run audit costs an afternoon of staff time. A specialist review costs more because it includes contract and data checks. Ask any adviser for a fixed fee and a written list of what it covers.
Who should carry out an AI audit?
Start internally, because your team know what they use. Bring in an independent adviser if personal data is involved, if you sell into the EU or if a client is asking questions. Independence matters because an adviser who sells software has a reason to find gaps that their product fills.
How often should a business run an AI audit?
In our view, every six months for most Businessses. AI tools and regulations both change quickly and a register that is a year old will already be wrong.
Where to start
An AI audit begins with knowing where your business stands. Take our free AI Readiness Assessment to get your readiness score and a personalised report in two to three minutes. Then use the afternoon test above to build your first register of tools.